NIS2 Quickscan
Know where you stand and what is left to do for NIS2.
NIS2 imposes stricter obligations around risk management and incident reporting. The responsibility sits explicitly with management. The NIS2 Quickscan gives you a clear picture of where you stand today and which steps will make your organisation secure and compliant.
Is your organisation ready for NIS2?
NIS2 is mandatory for organisations that play an essential or important role in the economy. The European directive imposes stricter requirements around risk management and incident reporting and expects you to be able to demonstrate a documented action plan and clear governance. The responsibility sits explicitly with management, which can be held personally liable in case of insufficient preparation. With our NIS2 Quickscan you get a clear picture of where you stand and which steps will make your organisation compliant.
Your situation tested against the NIS2 requirements
The Quickscan is a strategic risk analysis that tests your current situation against the NIS2 requirements. Through interviews and document reviews, complemented by a targeted technical check, we map your strengths, weaknesses and risks.
The objectives are:
Mapping your current level of NIS2 compliance
Identifying weaknesses, non-conformities and risks
Offering clear priorities and a roadmap towards compliance and stronger cyber resilience
To your action plan in three steps
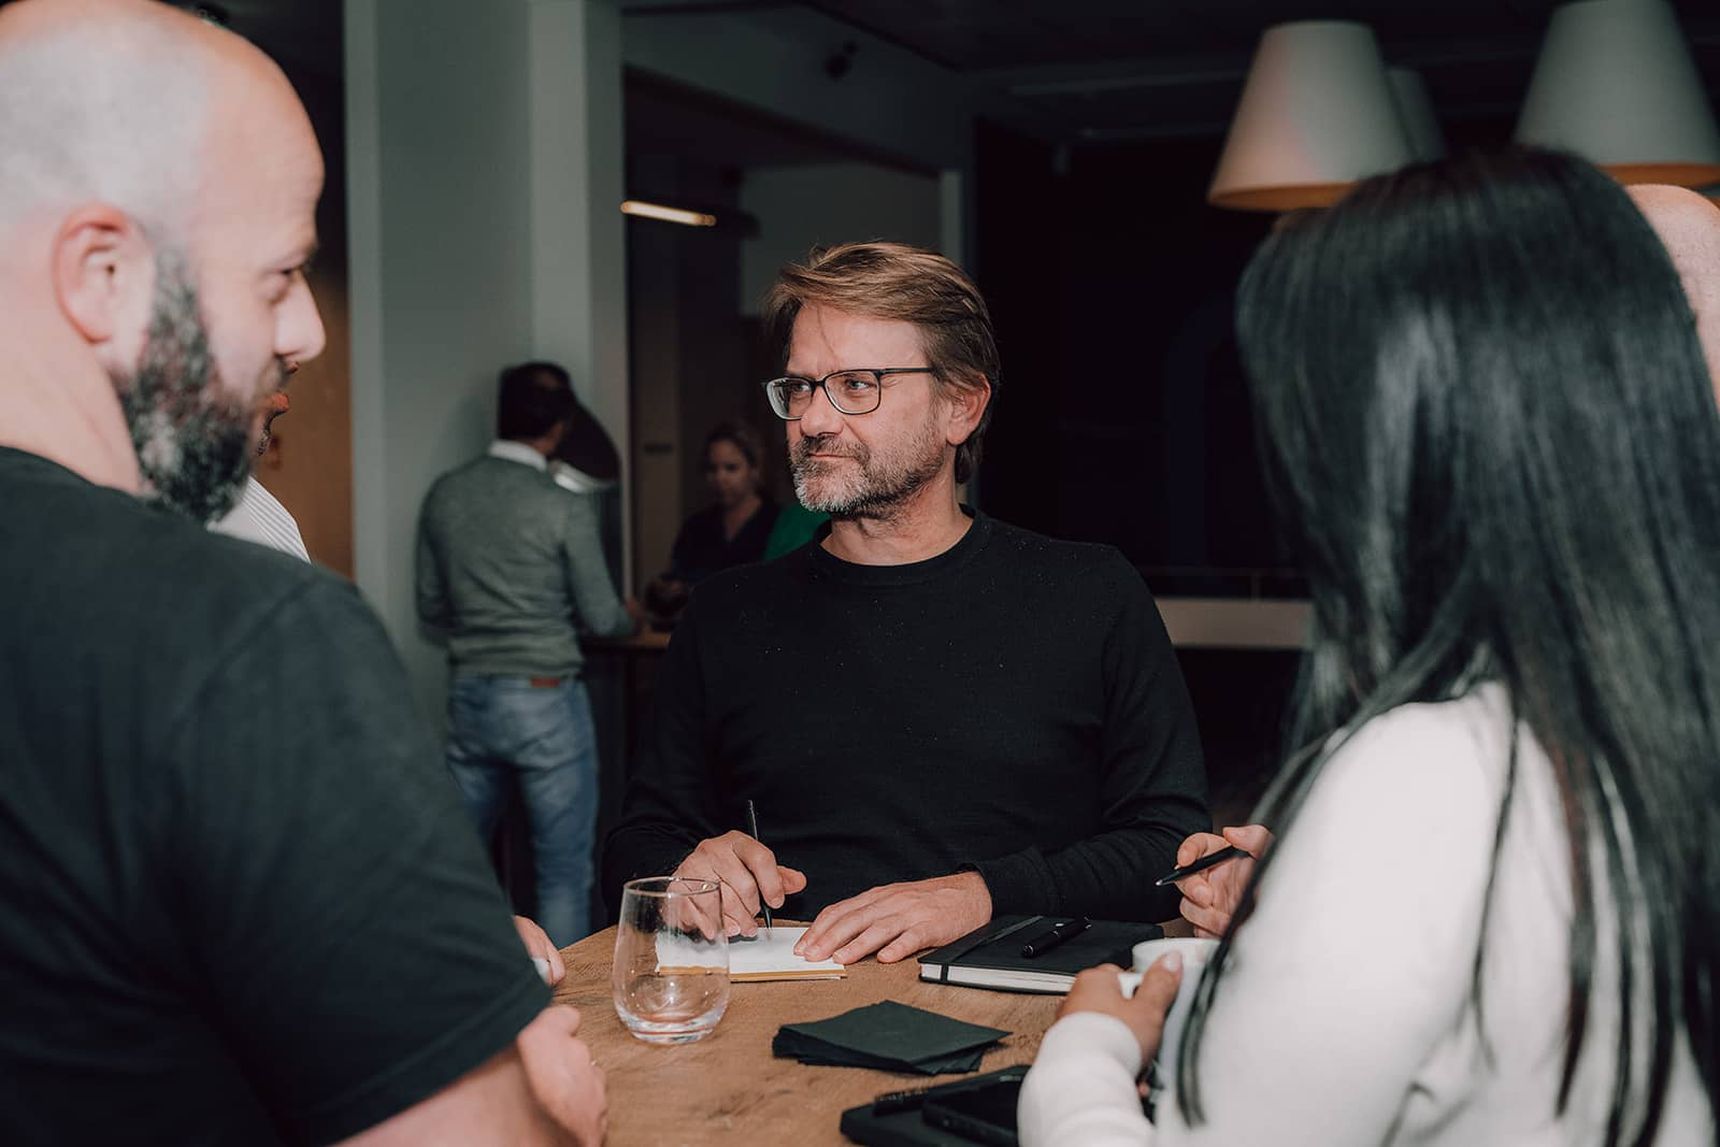
First we determine the scope of the scan together, aligned with the right stakeholders. Together we set out which security controls are most relevant for your organisation, with a realistic plan and clear milestones, so expectations are clear from the start.
Our experts come to you for in-depth interviews with your key stakeholders. They also go through your processes, policy documents and systems. In this phase we gather evidence, analyse the gaps and benchmark your current approach against the NIS2 requirements.
You receive a clear report that outlines your current level of compliance, maps risks and prioritises points for improvement. It comes with a practical remediation plan, an investment roadmap and input to update your IT security policy. That gives you a concrete path to compliance and resilience.
Beyond the Quickscan
The Quickscan is the beginning. You get a clear picture of your cybersecurity baseline and what is needed to go further. From there Xylos helps you turn insights into action, with targeted improvements such as:
Stronger resilience in your IT services, so your systems stay operational during incidents too
Reliable backup and recovery solutions that keep your downtime to a minimum
Next-level network security with Palo Alto, with advanced firewalls and threat prevention
Robust endpoint protection so employees work safely everywhere
Data governance and security to keep control over your information
24/7 monitoring and incident response
Cybersecurity awareness for employees
NIS2 awareness for management, in preparation for their liability
Ready to know your NIS2 status?
In an exploratory conversation our experts look at your situation and schedule your Quickscan.
The Quickscan fits into your wider approach
The NIS2 Quickscan is the first step in your Cybersecurity journey. With Managed Security you monitor your environment continuously afterwards. With the Cybersecurity Awareness Programme you make your people resilient too.
Questions about NIS2 and the Quickscan
The NIS2 law has applied since 18 October 2024 to organisations in 18 sectors, such as energy, transport, healthcare, digital infrastructure, food, chemicals and manufacturing. You are covered from 50 employees, or from an annual turnover and balance sheet total above 10 million euros. Depending on your sector and size, you are an essential or an important entity.
Even if you fall outside the law yourself, NIS2 can still affect you through customers who set requirements for their suppliers. Read more in our guide to NIS2 in Belgium.
The NIS2 Quickscan is a strategic risk analysis that assesses your current situation against the NIS2 requirements. Through interviews and document reviews, supplemented by a targeted technical check, we map your strengths, weaknesses and risks. That way you know where you stand and which steps make your organisation secure and compliant.
In three steps. In the pre-assessment, we jointly define the scope and the security controls that are most relevant to your organisation. During the on-site assessment, our experts interview your key stakeholders and review your processes, policy documents and systems. Finally, you receive the report and the action plan.
You receive a report that outlines your current compliance level, maps the risks and prioritises the points for improvement. It comes with a practical remediation plan, an investment roadmap and input to update your IT security policy.
Under NIS2, responsibility lies explicitly with management. The board approves the measures, oversees their implementation and must take training itself, and can be held personally liable if preparation falls short. That is why we also talk to your management during the Quickscan, and why we offer NIS2 awareness for management.
The Quickscan is the start of your cybersecurity journey. Xylos helps you turn the insights into targeted improvements, such as reliable backup and recovery, network security, endpoint protection and data governance. With Managed Security we then monitor your environment 24/7, and with the Cybersecurity Awareness Programme you make your employees resilient too.
Contact us
You will hear from us soon.